Best Encryption Tools to Buy in September 2026
The Mathematics of Secrets: Cryptography from Caesar Ciphers to Digital Encryption


2 Pcs Morse Code Challenge Coin, Encryption Message Training Coin for Radio
-
UNIQUE MORSE CODE ART: A CONVERSATION STARTER WITH ENCHANTING DESIGNS.
-
DURABLE KEEPSAKE: ANTIQUE BRONZE FINISH ENSURES LASTING QUALITY AND CHARM.
-
FUN LEARNING TOOL: TRANSFORM MORSE CODE EDUCATION INTO ENGAGING EXPERIENCES.
Practical Forensic Imaging: Securing Digital Evidence with Linux Tools
Foundations of Cryptography: Volume 1, Basic Tools
How to Find Out Everything About Anyone Online: The Complete Beginner’s Guide to OSINT Tools and Techniques (Practical Cybersecurity Toolkit Series)
10 Pcs White Household Hose Filters 8mm Water Pump Filters Stainless Steel Encryption Filters Garden Hose Strainer for Sprayers Car Washers Oil Pumps and Industrial Equipment Pumps and Circulation
- VERSATILE FILTRATION FOR SPRAYERS, CAR WASHERS, AND INDUSTRIAL TOOLS.
- UNIVERSAL FIT: PACK OF 10 FILTERS FOR SEAMLESS COMPATIBILITY.
- DURABLE STAINLESS STEEL DESIGN ENSURES LONG-LASTING FILTRATION PERFORMANCE.
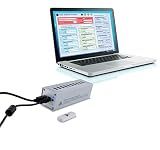
Apricorn Aegis Configurator On USB Key Bundled with Approved 10-Port USB Hub with 5 Amp Power Supply and Windows Based Software
- CONFIGURE 10 APRICORN DEVICES SIMULTANEOUSLY FOR EFFICIENCY.
- QUICK SETUP WITH AUTOMATIC ADMIN AND USER PIN CONFIGURATION.
- STORE LOG FILES FOR EASY RETRIEVAL OF SETTINGS AND RECOVERY PINS.
OFFENSIVE INTELLIGENCE: 300 techniques, tools and tips to know everything about everyone, in business and elsewhere
Building Cybersecurity Tools with Python: Create Your Own Scanners, Exploits, and Analysis Scripts
In order to enable CTR encryption in RocksDB, you first need to set up a custom encryption object that includes the encryption algorithm and key. This can be done by creating a new instance of rocksdb::BlockCipher and initializing it with the desired encryption algorithm and key. Once the encryption object is set up, you can then pass it to RocksDB when opening a database by setting the Encryption option to the encryption object that was created. This will enable CTR encryption for the database and protect the data stored in RocksDB using the specified encryption algorithm and key.
How to handle data corruption issues when using encryption in RocksDB?
Handling data corruption issues when using encryption in RocksDB involves implementing proper encryption and decryption processes, as well as using error detection and recovery mechanisms. Here are some steps to handle data corruption issues when using encryption in RocksDB:
- Use a strong encryption algorithm: Ensure that you are using a strong encryption algorithm to encrypt the data in RocksDB. This will help protect the data from unauthorized access and tampering.
- Implement proper encryption and decryption processes: Make sure that you have implemented proper encryption and decryption processes in your application code. This includes securely storing encryption keys, properly encrypting and decrypting data, and handling encryption errors.
- Use error detection mechanisms: Implement error detection mechanisms, such as checksums or hash functions, to detect any data corruption issues in the encrypted data. This can help you identify and mitigate data corruption issues before they cause more significant problems.
- Implement error recovery mechanisms: In the event of data corruption, implement error recovery mechanisms to restore the data to its original state. This may involve restoring the data from backups, re-encrypting the data, or other recovery processes.
- Monitor and audit data integrity: Regularly monitor and audit the integrity of the encrypted data in RocksDB to detect any potential data corruption issues. This can help you proactively address any issues before they become more significant problems.
By following these steps, you can effectively handle data corruption issues when using encryption in RocksDB and ensure the security and integrity of your data.
What is the role of key length in CTR encryption in RocksDB?
In CTR (Counter) encryption mode in RocksDB, the key length refers to the length of the encryption key used for encrypting and decrypting data. The key length is important as a longer key length generally provides higher security by making it harder for attackers to guess or brute force the key.
A longer key length in CTR encryption in RocksDB can increase the strength of the encryption algorithm and make it more resistant to various types of attacks, including brute force attacks and cryptographic attacks. It is recommended to use a key length that is appropriate for the level of security required for the data being encrypted.
In summary, the role of key length in CTR encryption in RocksDB is to determine the strength of the encryption algorithm and the level of security provided for the data stored in the database. A longer key length generally enhances security and is recommended for sensitive data.
What is the significance of nonce values in CTR encryption in RocksDB?
In CTR (Counter) mode encryption, a unique nonce (number used once) value is required for each encryption operation. This nonce value acts as a counter that is incremented for each block of plaintext that is encrypted, ensuring that the same plaintext block encrypted with the same key will produce a different ciphertext each time.
In RocksDB, the nonce values are used to prevent encryption key reuse, which can lead to security vulnerabilities such as leaking information about the plaintext or the key itself. By using unique nonce values for each encryption operation, RocksDB ensures the security and integrity of the data being encrypted and decrypted.
In summary, the significance of nonce values in CTR encryption in RocksDB is to prevent key reuse and ensure the security of the encrypted data.